ANSHUMAN
PANDEY
I build digital experiences, security systems and things that shouldn't look boring.
BUILDING SOLUTIONS
CREATING IMPACT
I LIKE BUILDING
THINGS THAT
MAKE PEOPLE
LOOK TWICE.
I'm a BCA graduate focused on Cybersecurity and SOC operations. I enjoy analyzing threats, investigating incidents, and building practical security solutions.
 PROFILE / 2026
01 / SYSTEM STATUSDEFENDING THE
DIGITAL LAYER.Monitoring signals. Investigating threats.
Learning how attacks move — and how to stop them.STATUS: BUILDING // MODE: BLUE TEAM
WHAT I
WORK WITH
Curious by default. Practical by design.
Always one layer deeper.
SELECTED WORK.
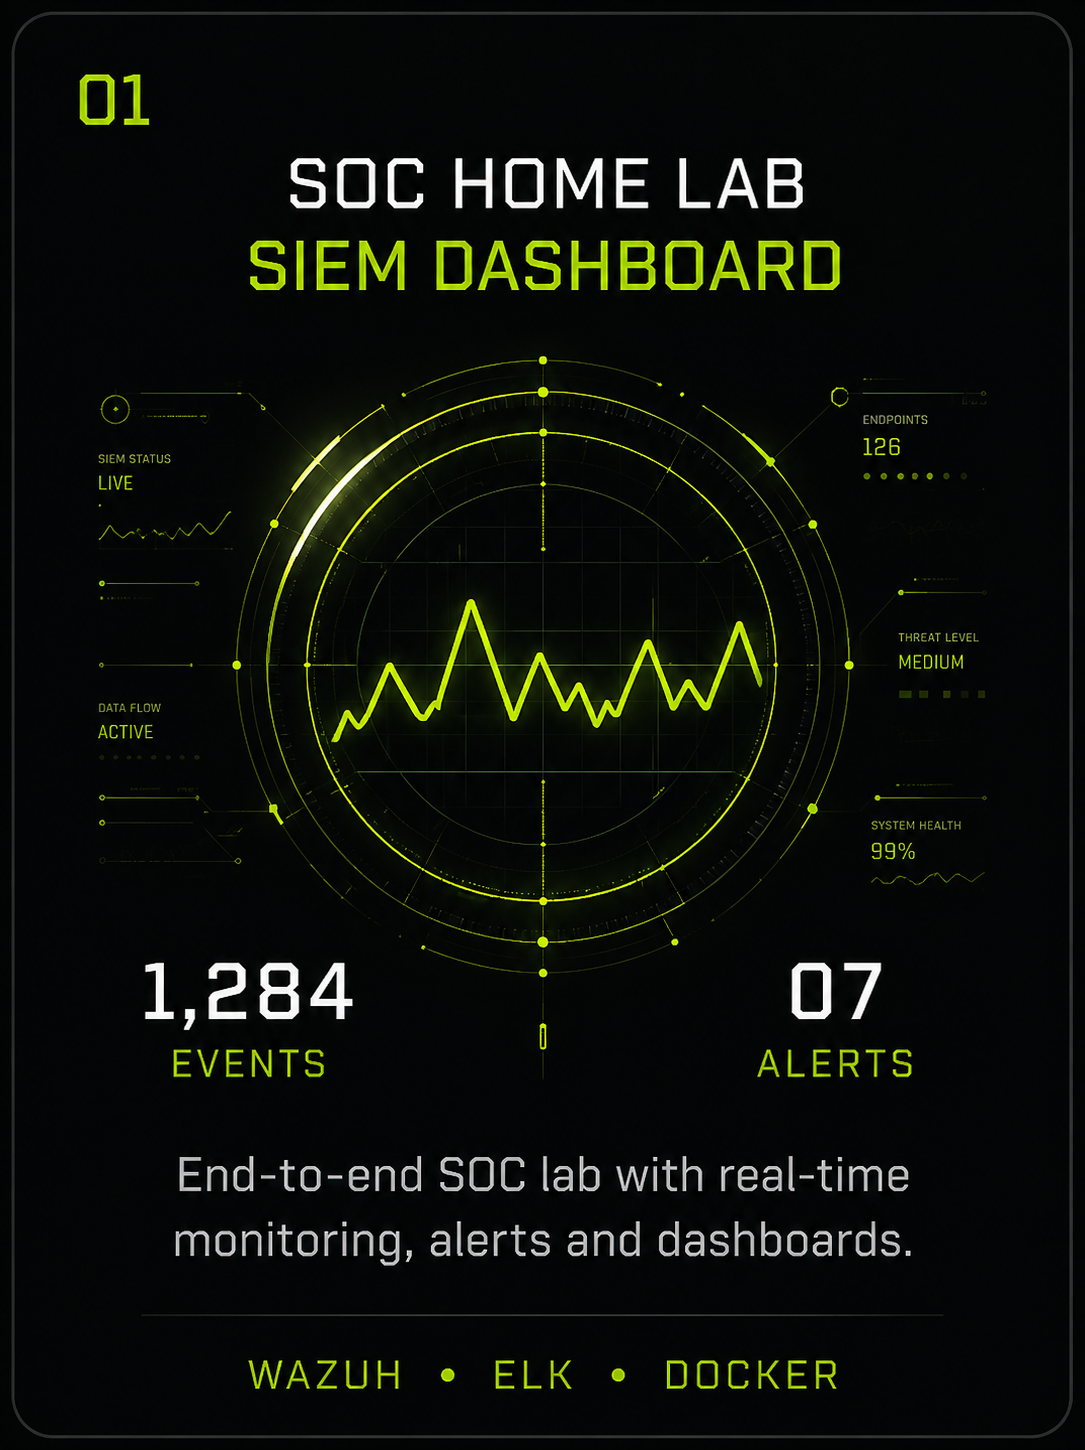
SOC HOME LAB / SIEM DASHBOARD
A practical Security Operations environment for monitoring, detection, SIEM workflows and incident investigation.
EXPLORE PROJECT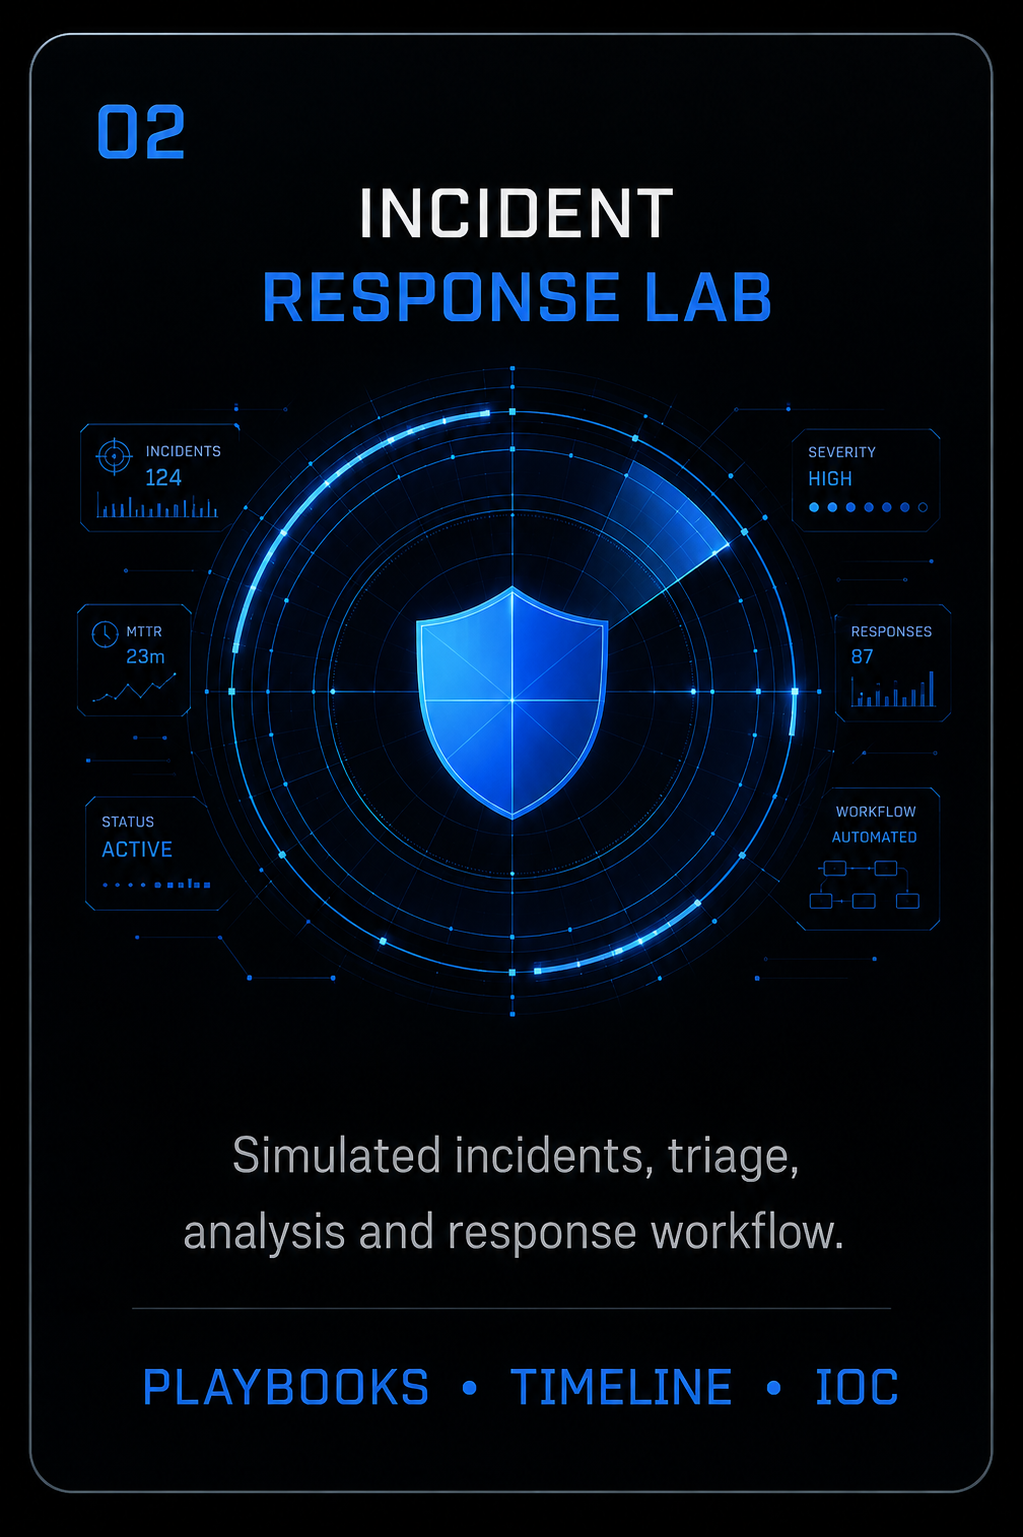
INCIDENT RESPONSE & INVESTIGATION PLATFORM
A structured platform for alert triage, investigation, evidence handling, timelines, IOCs and incident response workflows.
EXPLORE PROJECT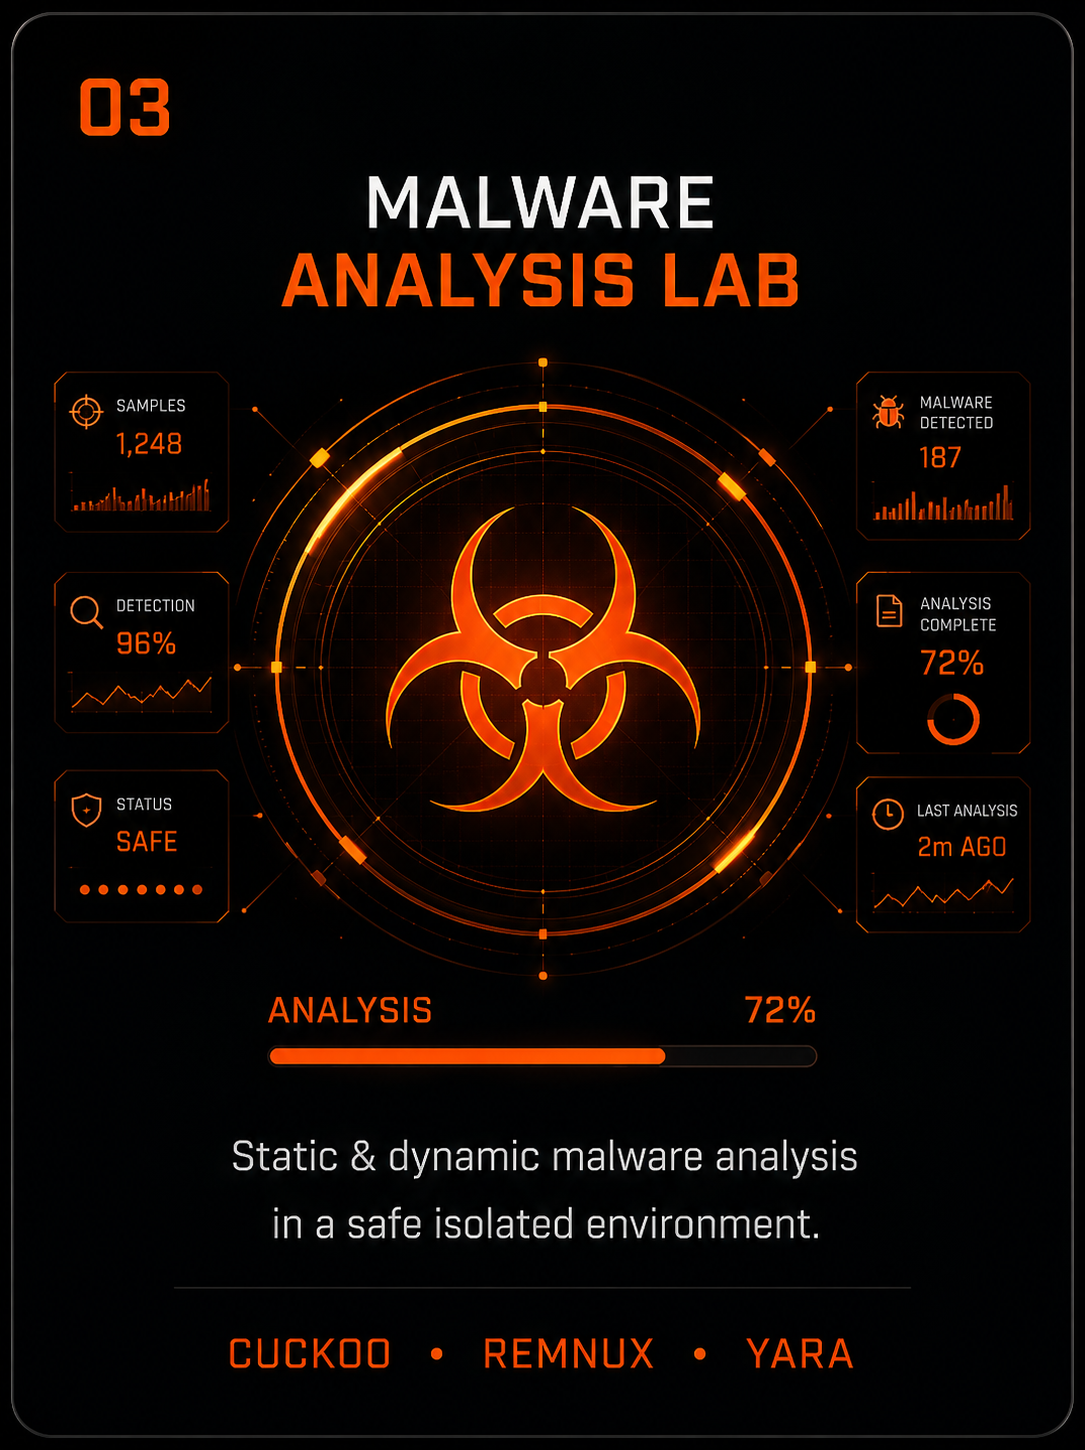
MALWARE ANALYSIS SANDBOX
An isolated malware-analysis environment for safe static analysis, behavioral observation, network monitoring and IOC extraction.
EXPLORE PROJECT
NETWORK IDS & SECURITY MONITORING
A network-defense lab for traffic visibility, intrusion detection, suspicious activity monitoring and alert investigation.
EXPLORE PROJECT
MITRE ATT&CK ATTACK SIMULATION LAB
An authorized lab for simulating defensive-security scenarios, generating telemetry and mapping observed behavior to MITRE ATT&CK.
EXPLORE PROJECT
AI SECURITY ASSISTANT / SOC COPILOT
An AI-assisted security workspace for alert explanation, log analysis, IOC extraction, investigation guidance and report generation.
EXPLORE PROJECTMICRO PROJECTS.
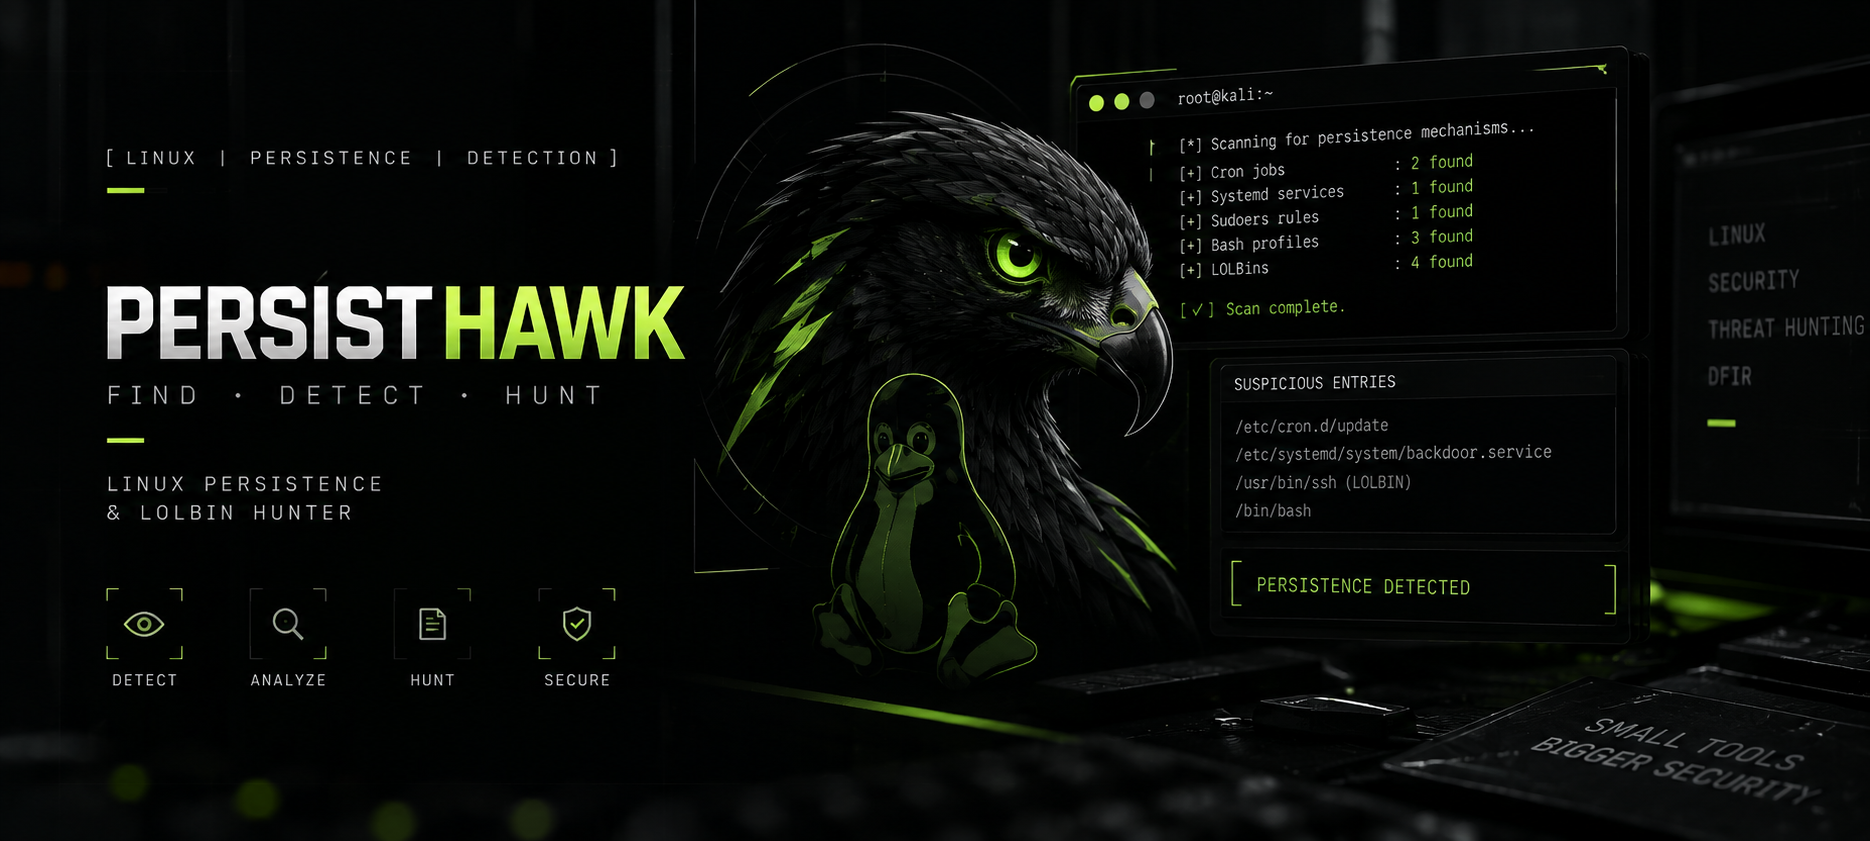
PersistHawk
Linux Persistence & LOLBin Hunter
Detects persistence mechanisms and abnormal LOLBin usage on Linux.
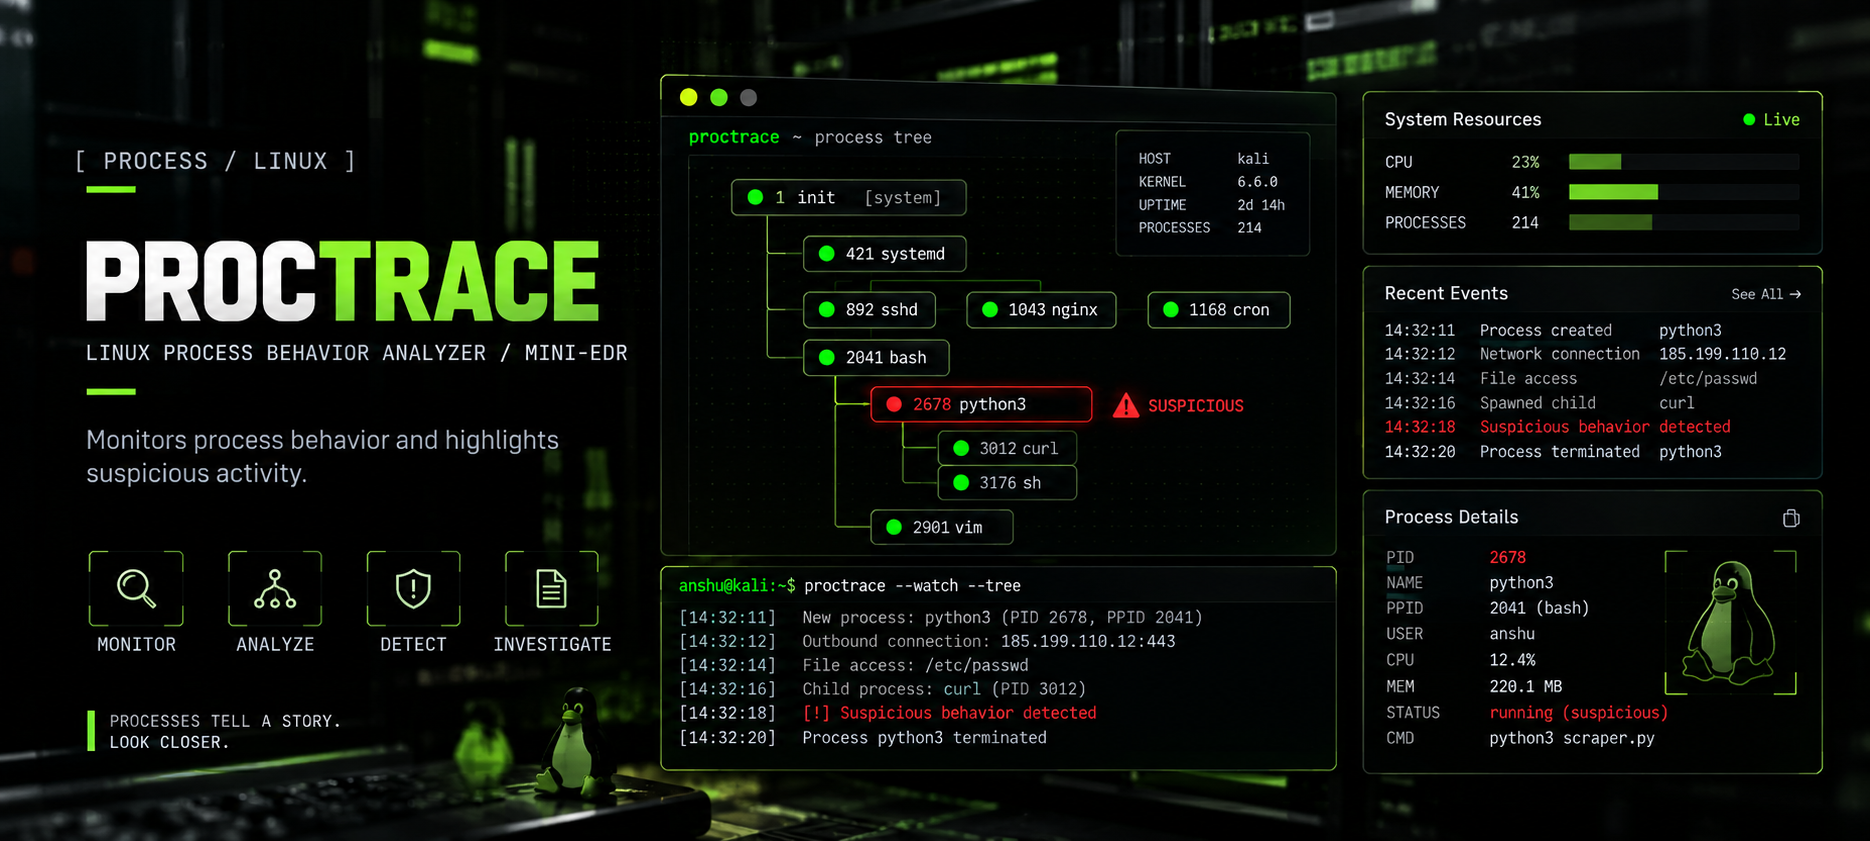
ProcTrace
Linux Process Behavior Analyzer / Mini-EDR
Monitors process behavior and highlights suspicious activity.
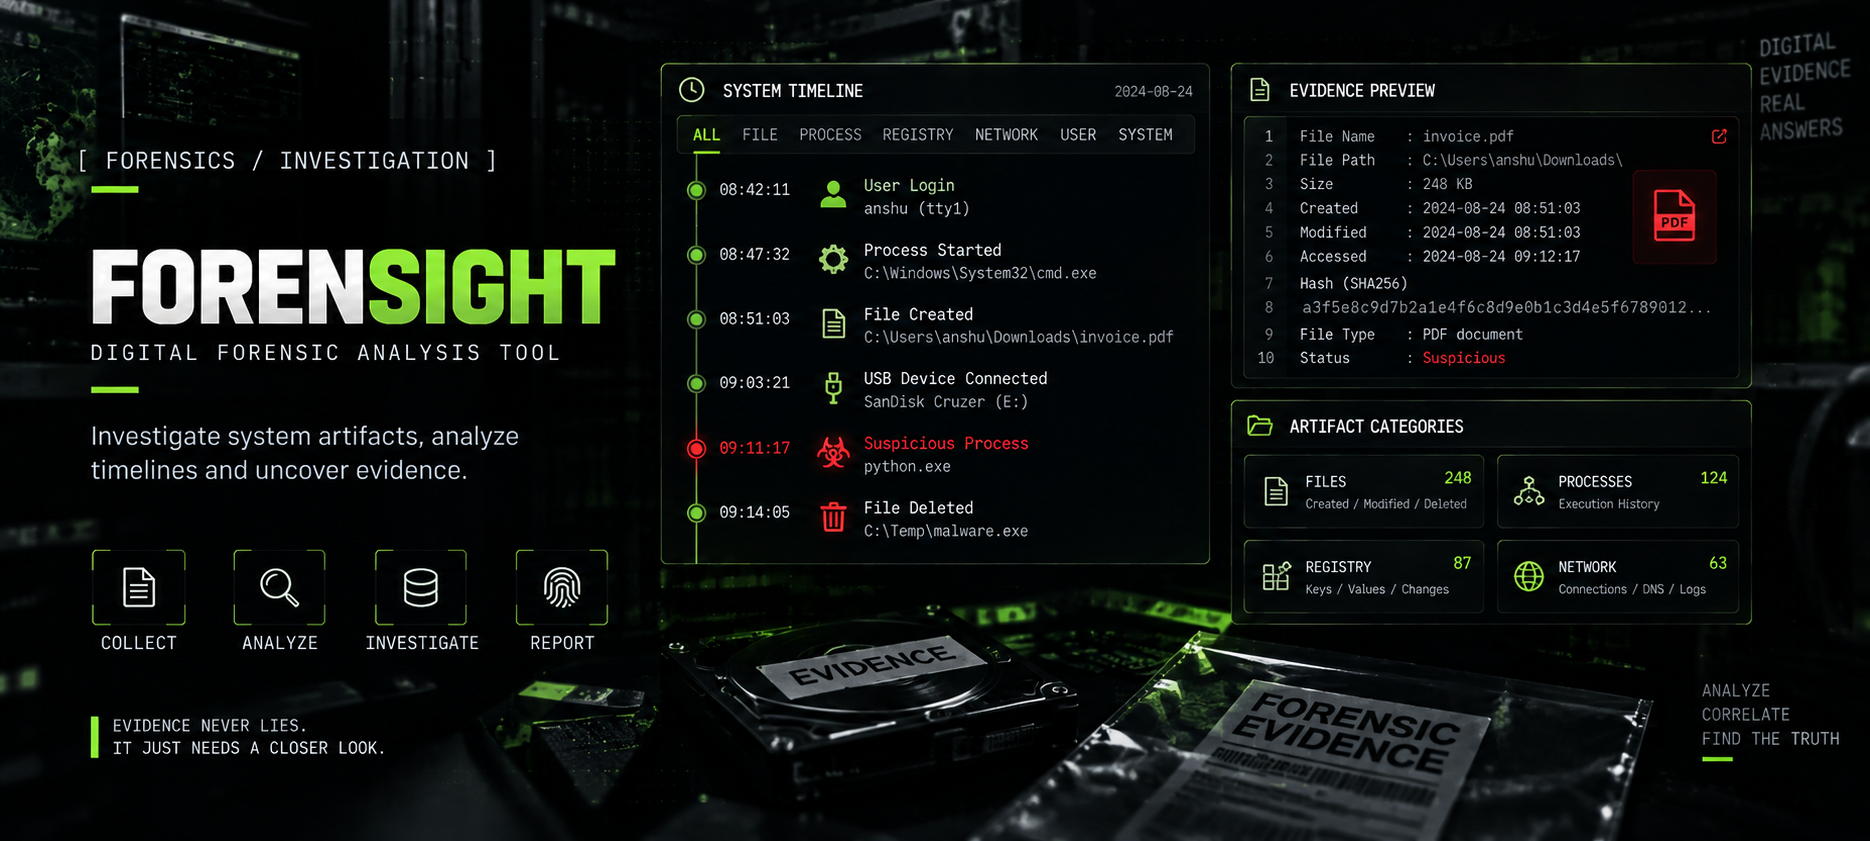
ForenSight
Linux DFIR Evidence & Timeline Engine
Collects evidence, builds timelines and supports forensic investigation.
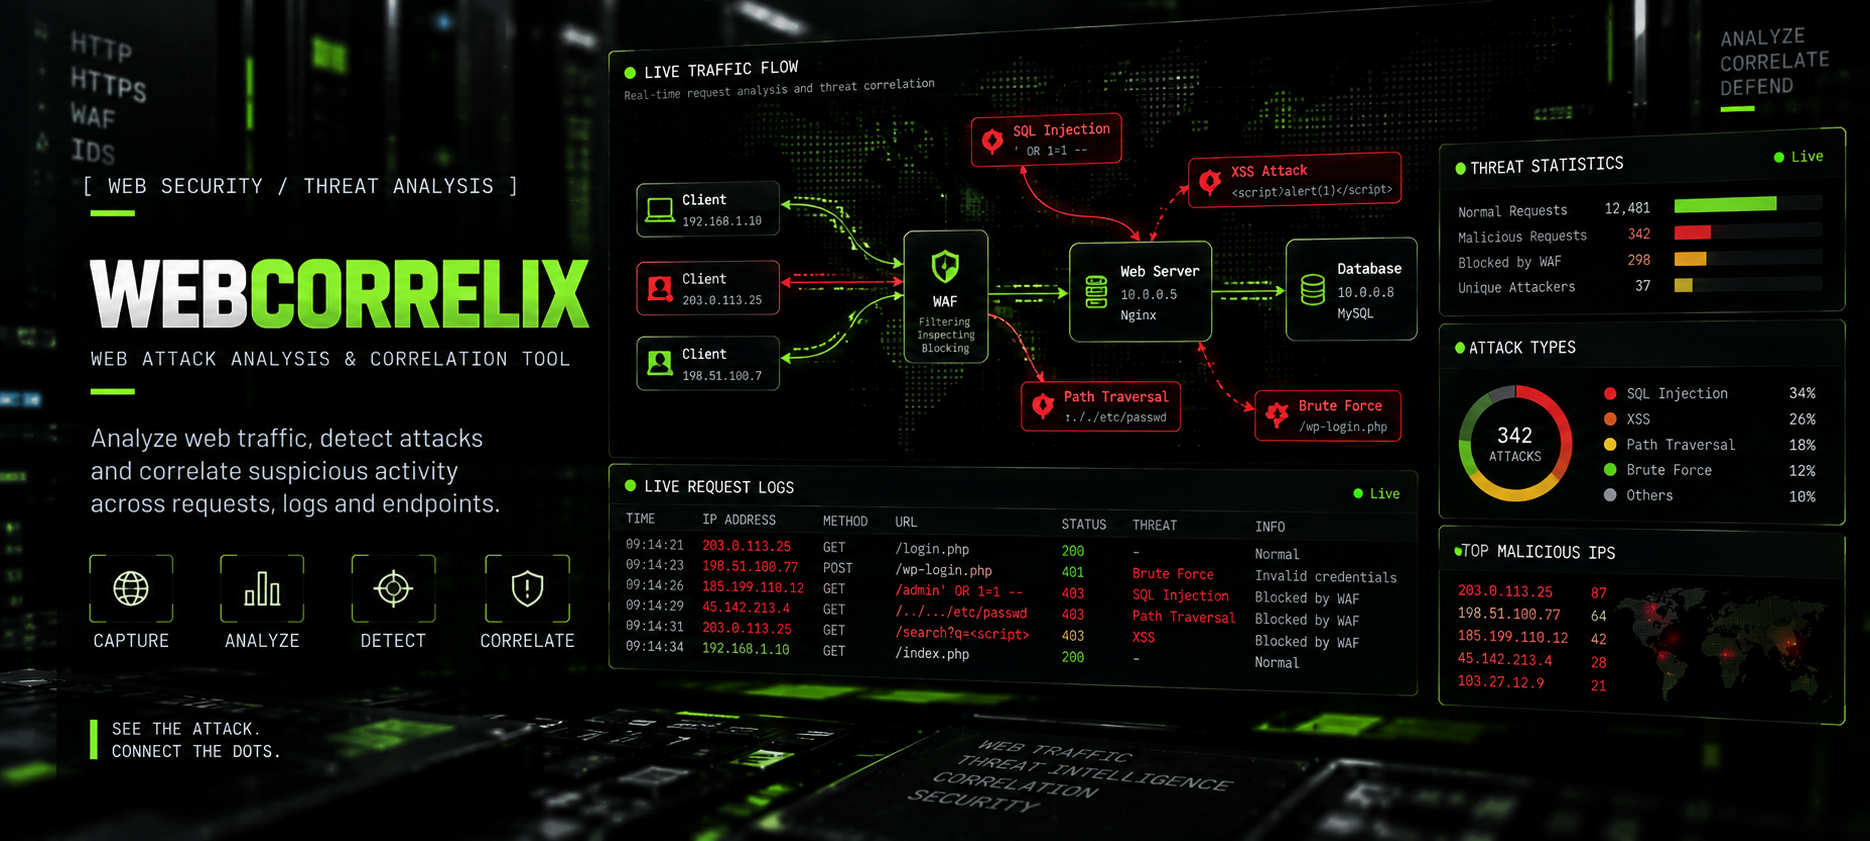
WebCorrelix
Web Attack Detection & Correlation Engine
Analyzes web activity and correlates attack patterns for faster triage.
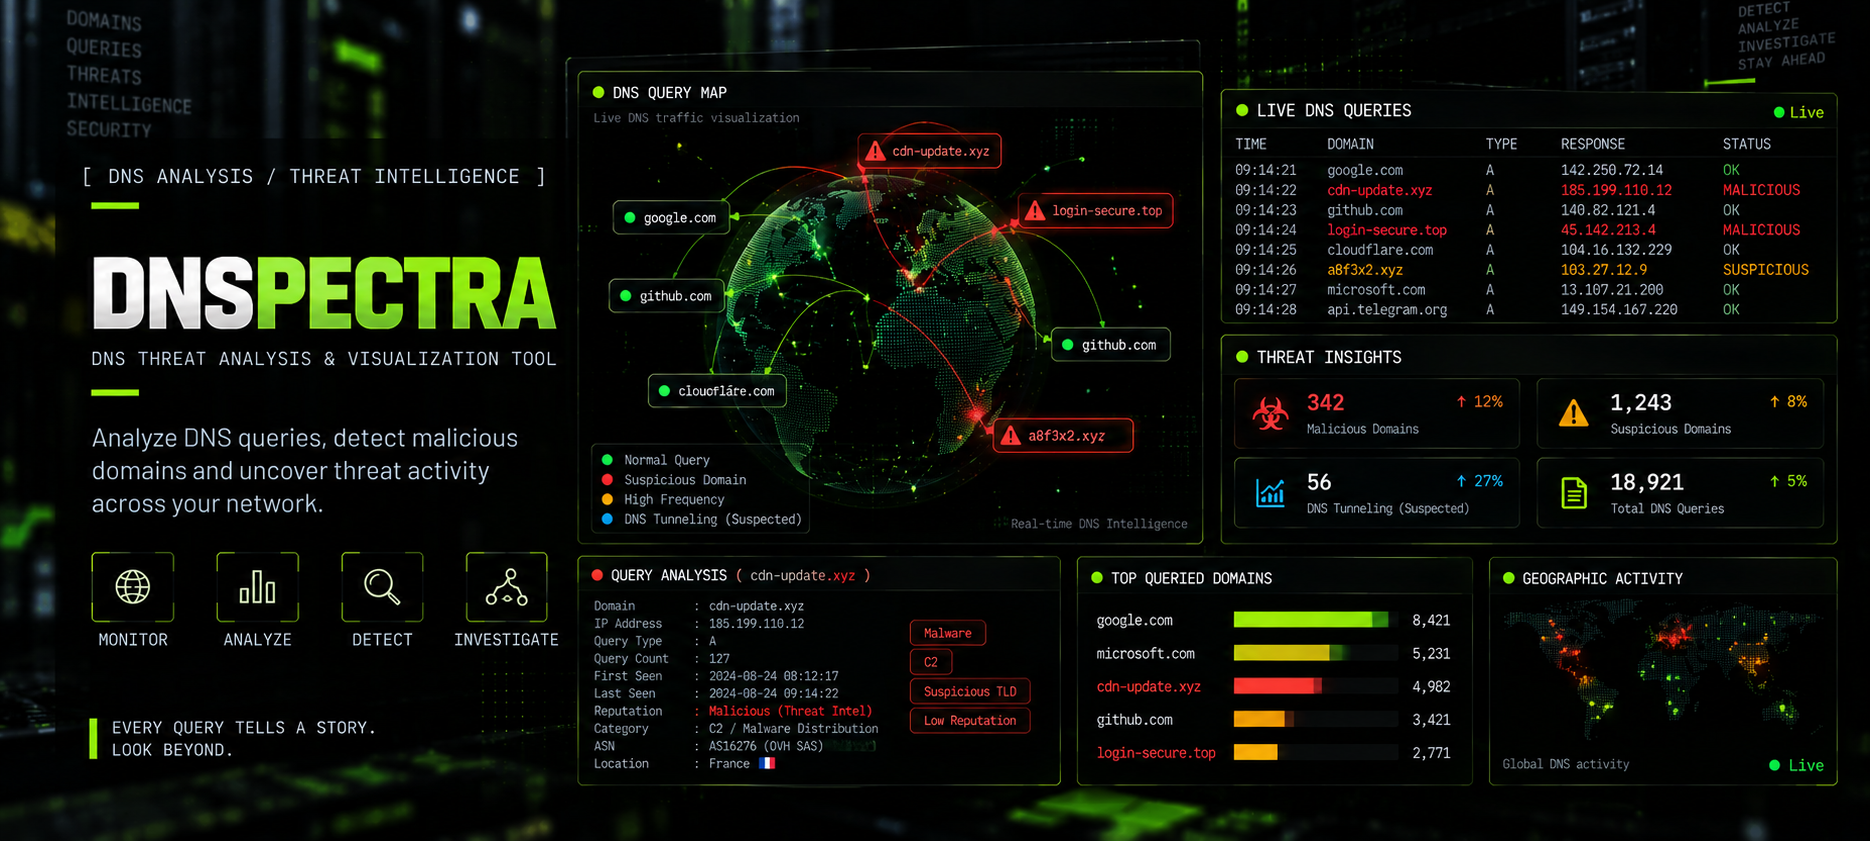
DNSpectra
Linux DNS Threat Hunting Engine
Analyzes DNS traffic and logs to identify suspicious domains and anomalies.
BUILD.
BREAK.
LEARN.
Small systems, interfaces and security experiments.
Because learning should be visible.
ALWAYS
LEARNING.
CURRENT FOCUS / CYBERSECURITY + SOC
EXPLORING NEXT